Analysis
We review your processes, IT systems and existing security measures and clarify which obligations apply to you. At your company or via video call, you decide.
Fit/gap analysisService: IT security
From ISMS implementation to NIS-2, ISO 27001 and TISAX through to SIEM, phishing campaigns, awareness and emergency planning: machCon supports companies across the DACH region holistically.
Self-test: can you withstand ten waves of attacks?Guide
You do not need to know what the right service is called. Choose the situation that fits you best.
Your situation is not listed?
In the initial consultation we find out where you should start.
Free initial consultationOur services
A dedicated contact takes on the role of information security officer for you, reports to management and keeps your ISMS running at all times.
External information security officerWe build your information security management system (ISMS) and maintain it continuously. The first steps are roles, risk analysis and policies suited to the size of your company. Regular risk assessments, internal audits, management reviews and tracking of measures keep your ISMS up to date. This keeps you audit-ready and prepared for ISO 27001, NIS-2 and TISAX.
Realistic phishing simulations show where your team stands and train the weak spots in a targeted way.
To phishing campaignsPractical training turns your employees into the first line of defence against social engineering.
Emergency manual, recovery plans and exercises so that critical processes keep running even in an emergency.
We set up a SIEM that collects and analyses security-relevant events centrally and makes attacks visible early.
Scoping assessment, action plan and ongoing support so that you can demonstrably meet your NIS-2 obligations.
To NIS-2 implementation and supportFor manufacturers of products with digital elements: we translate the requirements of the CRA into concrete steps.
To the Cyber Resilience ActOur approach
Information security is not a one-off project. Every service has its fixed place, and you can join in the phase where you want support.
We review your processes, IT systems and existing security measures and clarify which obligations apply to you. At your company or via video call, you decide.
Fit/gap analysisBased on the analysis, we create the structures and technology that support your information security in the long term, prioritised by risk and effort.
Prioritised implementationYou demonstrate to customers, partners and authorities that your measures work. We prepare you specifically for audit and assessment.
Audit-readyWe maintain your security level, train your team and adapt everything to new threats. Insights feed directly into the next analysis.
Continuous improvementWe talk to you and find out what matters to you. Depending on that, we are happy to run workshops, audits and support on site or remotely via video call. We support companies throughout Germany, Austria and Switzerland.
Standards and regulation
Which requirement applies to whom, is it mandatory, and what exactly do you have to do? The key frameworks at a glance.
| Framework | Who is affected | Mandatory or voluntary | What needs to be done | Our service |
|---|---|---|---|---|
| NIS-2EU directive, implemented in Germany by the NIS2UmsuCG and in Austria by the NISG 2026 | Companies from 18 sectors, usually with 50 or more employees or EUR 10 million annual turnover. Some entities regardless of size. | Legal obligationGermany: in force since 6 December 2025. Austria: in force since 1 October 2026. | Registration with the BSI, risk management, reporting of significant incidents (early warning within 24 hours), training and accountability of management. | NIS-2 implementation and support |
| ISO/IEC 27001International standard for information security management systems | Companies of any size and industry that want to manage and demonstrate their information security systematically. | VoluntaryOften required by customers | Build an ISMS, assess risks, implement measures, carry out internal audits, certification by an accredited body. | ISO 27001 support |
| TISAXAssessment and exchange mechanism of the automotive industry (VDA / ENX) | Suppliers and service providers working for car manufacturers with confidential information, prototypes or personal data. | Market requirementContractually required | Self-assessment according to VDA ISA, close gaps, assessment by an approved audit provider, share the label in the ENX portal. | TISAX support |
| Cyber Resilience ActEU regulation for products with digital elements | Manufacturers, importers and distributors of hardware and software with digital elements placed on the EU market. | Legal obligationReporting obligations from 11 September 2026, full application from 11 December 2027. Applies directly across the EU, identically in Germany and Austria. | Security by design, risk assessment per product, vulnerability management across the life cycle, reporting of actively exploited vulnerabilities, technical documentation. | Cyber Resilience Act |
Several requirements at once?
Many requirements overlap. An ISMS according to ISO 27001 is a good basis for NIS-2 and TISAX, so you avoid duplicate work.
As of: October 2026
Industries
Every industry has its own requirements. We know the rules that apply to you and implement them to suit your business.
Anyone working for manufacturers with confidential data or prototypes usually needs a TISAX label. Many suppliers also fall under NIS-2.
TISAX supportMachines and devices with software or network connectivity fall under the Cyber Resilience Act. Mechanical engineering is also an NIS-2 sector.
Cyber Resilience ActElectricity, gas, heating, drinking water and waste water are among the highly critical sectors and are a particular focus of supervision.
NIS-2 implementationHospitals, laboratories and medical device manufacturers must demonstrably ensure the availability and confidentiality of sensitive data.
NIS-2 implementationProduction, processing and distribution are NIS-2 sectors. Production outages quickly affect entire supply chains.
Business continuityManaged service providers, data centres and platforms are often affected regardless of their size and are asked by customers for evidence.
ISO 27001 supportInformation security affects every industry. We know the typical risks and speak your language.
Why machCon
Information security is not a one-off project but a continuous process. With machCon you have experienced security experts at your side who act proactively, detect risks early and keep you up to date.
Meet our team
350+
companies supported
Our consultants hold recognised qualifications in information security and keep their knowledge continuously up to date.
Our internal processes are certified according to ISO 9001. We attach great importance to consistently high consulting quality for you.
Every client has a personal main contact and a dedicated deputy who know your company and your IT landscape. On site or remote, just as you prefer.
A large part of our team works in Engen in the Hegau region. From here we can quickly reach companies in Singen, Konstanz, Radolfzell, Stockach, Tuttlingen, Villingen-Schwenningen or Schaffhausen, and we are happy to come to you for audits, training and workshops.
In Zug and Basel we are right in the middle of one of Switzerland’s most important business regions. Here our consultants usually work directly at your company and are firmly integrated into your projects. Our clients come from a wide range of industries, from pharma and life sciences to local authorities. We support them in a wide variety of projects and provide ongoing support for data protection, IT security and quality management.
We support clients throughout Germany, Austria and Switzerland just as reliably, with dedicated contacts, remote meetings and on-site visits whenever they are needed.
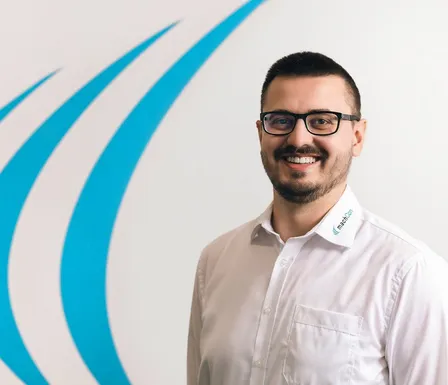
Zdravko Matić
IT Security Consultant
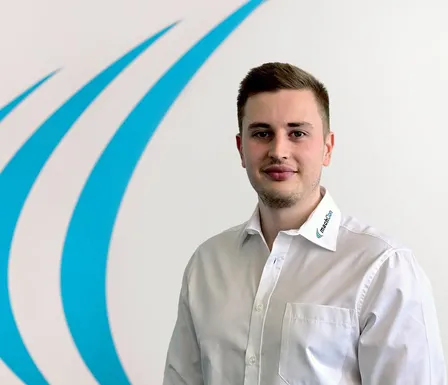
Stanislav Miller
IT Security Consultant
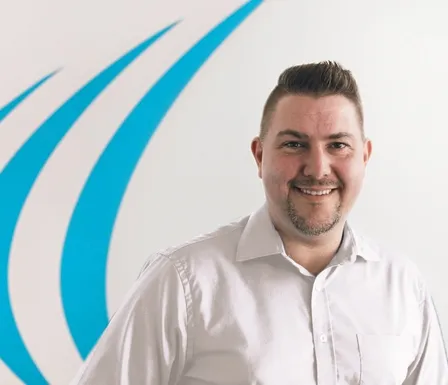
Christian Herbst
Managing Director and Owner, machCon Group
Dipl. Computer Scientist, BSc, PMP
Customer reviews
Companies achieving their goals in IT security, NIS-2 and compliance with machCon.
“Working with machCon exceeded our expectations.
Their expertise and tailored solutions have significantly improved our security infrastructure, and they help us understand and take the NIS-2 measures we need. Their professional and proactive approach has won us over!”
 FSM AGClient
Become our next success story
In a free 30-minute initial consultation we clarify what your company needs in IT security.
Book a consultation“Thanks to machCon's NIS-2 and IT security consulting, we were finally able to get our bearings and significantly optimise our IT security measures. Through professional consulting and solutions tailored to our specific needs, we feel ready and secure. We recommend their services without reservation.”
 Renfert GmbHClient
“Thanks to machCon's NIS-2 and IT security consulting, we have significantly improved our security measures. Their expertise and tailored solutions have helped us meet NIS-2 requirements without any issues. We particularly appreciate their straightforward and dedicated way of working. We are very satisfied and happy to recommend machCon as a partner.”
 Fidel Dreher GmbHClient
Related services
Information security touches many areas of your company. These topics complement it ideally and can be implemented with us from a single source.
Information security and data protection go hand in hand. As external data protection officer we ideally complement the information security officer, both roles coordinated from a single source.
Data protection consultingAnyone using AI needs clear rules for data, risks and responsibility. We support you in implementing the EU AI Act and secure AI governance.
AI complianceAn ISMS according to ISO 27001 and a QMS according to ISO 9001 combine excellently. This lets you use synergies in processes, documentation and audits.
Quality managementNIS-2 obliges many companies to implement risk management, reporting processes and management accountability. We check whether you are affected and implement the obligations step by step.
NIS-2 implementationAnyone manufacturing or distributing products with digital elements must demonstrate security by design, vulnerability management and reporting. We translate the CRA into concrete steps for your products.
Cyber Resilience ActMost attacks start with an email. With realistic phishing simulations and practical awareness training, we turn your employees into the first line of defence.
Phishing awarenessFAQ
The key answers on ISMS, NIS-2, ISO 27001, TISAX and protecting your company.
Your question is not listed?
In a free 30-minute initial consultation we answer your questions personally, on site or remotely.
Book a consultationThe basis consists of clear responsibilities, a risk analysis, regular backups, patch and access management, multi-factor authentication and trained employees.
Which further measures are needed depends on industry, size and legal requirements. An information security management system (ISMS) ensures that measures are prioritised, documented and reviewed regularly.
To get a feel for choosing the right measures at the right time on a tight budget, try our card game Breach.
IT security protects IT systems, networks and digital data. Information security is broader and protects all of a company’s information, whether digital, on paper or in the knowledge of employees.
Cybersecurity refers to the part that specifically targets attacks from the internet. Standards such as ISO 27001 and laws such as NIS-2 are based on information security.
An information security management system (ISMS) is a framework of policies, processes and responsibilities with which a company manages its information security in a planned way and continuously improves it.
It includes a security policy, risk analysis and treatment, internal audits and management reviews, among other things. The best-known basis is ISO/IEC 27001; in Germany, BSI IT-Grundschutz is also used.
As a rule, companies from one of the 18 NIS-2 sectors with at least 50 employees or more than EUR 10 million annual turnover are affected. Some entities, such as certain digital services, fall under it regardless of their size.
In Germany the NIS2UmsuCG has applied since 6 December 2025, in Austria the NISG 2026 since 1 October 2026. Affected companies must register with the competent authority and implement risk management and reporting processes. Our NIS-2 scoping assessment quickly provides clarity.
You need TISAX if a customer from the automotive industry requires it, usually because you work with confidential information or prototypes. ISO 27001 is the cross-industry standard and suits anyone who wants to demonstrate their information security in an internationally recognised way.
Both are based on similar requirements. Running an ISMS according to ISO 27001 gives you a good basis for TISAX, and vice versa.
Phishing simulations work best when they take place regularly throughout the year rather than as a one-off. This keeps awareness permanently high and makes progress measurable.
In addition, new employees should be trained during onboarding.
An emergency manual defines who does what in an emergency: reporting channels, responsibilities, immediate measures and recovery plans for critical processes and systems.
It is a central part of business continuity management. To work in an emergency, it should be practised and updated regularly.
The Cyber Resilience Act applies to manufacturers, importers and distributors of products with digital elements, i.e. hardware and software placed on the EU market.
As an EU regulation it applies directly and uniformly in Germany and Austria. Reporting obligations for actively exploited vulnerabilities apply from 11 September 2026, the remaining obligations from 11 December 2027. Swiss manufacturers are also affected as soon as they sell products in the EU.
An external information security officer (ISO) manages and monitors your company’s information security on behalf of management, without you having to create a dedicated position.
They build and maintain the ISMS, assess risks, coordinate security incidents and report regularly to management.
In 30 minutes we clarify free of charge and without obligation which requirements apply to you, where your biggest gaps are and which route is the most economical.